DMARC (Domain-based Message Authentication, Reporting, and Conformance) is an email authentication and reporting protocol that helps prevent email spoofing, phishing, and other fraudulent activities by allowing domain owners to set policies for email sources (such as email providers, e.g. Yahoo Mail, Outlook and Gmail, etc.) on how to handle emails that claim to be from their domain. DMARC works alongside SPF and DKIM to verify the authenticity of incoming emails and enables domain owners to specify actions for unauthenticated emails, such as quarantining or rejecting them. This enhances email security and protects both senders and recipients from potential email-based attacks.
In 2007, SPF and DKIM were separately introduced to help combat email abuse and improve email deliverability. SPF focused on preventing sender address forgery, while DKIM added cryptographic signatures to emails to verify their authenticity. DMARC was proposed by a group of organisations, including PayPal, Google, Microsoft, Facebook, and Yahoo, to provide a standardised framework for email authentication and reporting in 2012. The goal was to bring together SPF and DKIM to enhance email security and reduce domain spoofing. From 2012 to 2015, DMARC gained traction among email service providers and domain owners as a solution to prevent email-based attacks. Major email providers like Google and Microsoft began to support DMARC policies. Since 2015, DMARC adoption continued to grow, and it has become an essential tool in the fight against phishing and email fraud. Organizations across various industries, including financial services, government, and technology, embraced DMARC to protect their domains and users.
DMARC allows domain owners to publish policies that specify how email receivers should handle messages that fail authentication checks. It also provides valuable feedback through reporting mechanisms, allowing domain owners to monitor and analyse email activity related to their domains. It has played a pivotal role in improving email security, reducing domain impersonation, and enhancing the trustworthiness of digital communication. Its adoption continues to expand as businesses and organizations recognize its significance in safeguarding their online communications.
DMARC enhances email security, authenticity, and control while providing valuable insights to domain owners for maintaining a secure and reliable email ecosystem.
Here are the key benefits:
Without DMARC, organizations are more susceptible to various risks related to email security and brand reputation.
Some of the key risks include:
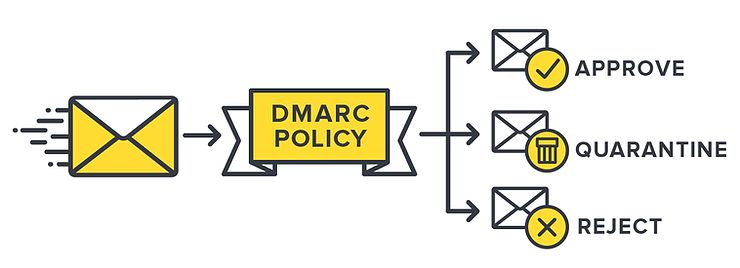
The DMARC policy is a set of instructions that domain owners define to specify how email receivers (such as email providers) should handle incoming emails claiming to be from their domain. The policy can be set to one of three possible actions:
SPF validates the sending mail server's IP address against the authorised list in the domain's SPF record, while DKIM verifies the integrity of the email's content using cryptographic signatures. SPF and DKIM are often used together with DMARC (Domain-based Message Authentication, Reporting, and Conformance) to provide comprehensive email authentication and protection against email spoofing and phishing attacks.
| SPF (Sender Policy Framework) | DKIM (DomainKeys Identified Mail) |
|---|---|
| SPF is a simple email authentication protocol that relies on DNS (Domain Name System) records. | DKIM uses cryptographic signatures to validate the integrity of the email's content and ensure that it hasn't been altered during transit. |
| When an email is received, the recipient's email server checks the SPF record of the sender's domain to verify if the sending mail server is authorized to send emails on behalf of that domain. | When an email is sent, the sender's domain adds a digital signature to the email header using a private key, which is stored in the domain's DNS records. |
| The SPF record contains a list of IP addresses or hostnames that are allowed to send emails for the domain. If the sender's IP address matches one of the entries in the SPF record, the email is considered authenticated. | When the email is received, the recipient's email server retrieves the public key from the sender's domain DNS and verifies the signature. If the signature is valid, it confirms that the email's content remains unchanged since it was signed. |
| SPF primarily validates the envelope sender, which is used in the SMTP (Simple Mail Transfer Protocol) communication, but not the content of the email itself. | DKIM focuses on validating the content of the email and provides a level of assurance that the email is from the claimed sender and hasn't been tampered with. |
All organisations should implement DMARC, so any organisation is a potential client for this managed service, especially those that use 3rd parties to send emails to staff and/or customers. Organisations that invest in email marketing (e.g. Retail, B2C, and others) rely heavily on successfully delivering emails to their customers. For them, DMARC-compliant emails have significantly higher delivery rates.
Organisations using this service will have visibility to:
How Can Spartans Security Help?
Spartans Security helps businesses by providing a managed service that enables clients to achieve and maintain DMARC compliance.
The service aggregates the DMARC email reports for a client’s domains and details DMARC compliance per email source. The service also identifies issues and non-compliant email source details in the form of tasks and the remediation required to maintain or enable a DMARC reject policy per domain.
With the reject policy applied, it becomes impossible for the email from that domain to be spoofed, protecting the client and their staff and customers from this common and very successful form of phishing.
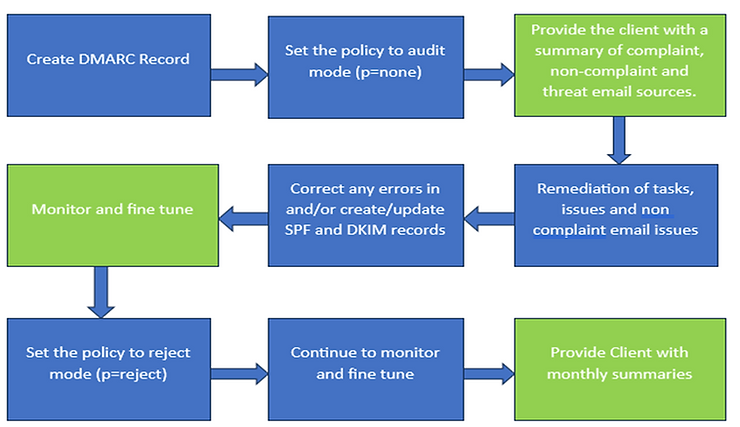
The following per-domain service flow shows DNS changes and remediation in blue and the DMARC managed service in green.
In summary, SPF validates the sending mail server's IP address against the authorised list in the domain's SPF record. At the same time, DKIM verifies the integrity of the email's content using cryptographic signatures. SPF and DKIM are often used with DMARC (Domain-based Message Authentication, Reporting, and Conformance) to provide comprehensive email authentication and protection against email spoofing and phishing attacks. In DMARC, alignment is crucial. It demands that the domains authenticated by SPF or DKIM match the domain in the email's From header. Unlike SPF and DKIM, which don't directly relate to the From address, DMARC ensures this alignment. If the domains don't match, DMARC fails, providing vital control against phishing and unauthorized domain use.